If it can happen to Binance’s engineers, it can happen to anyone
In October 2026, attackers pulled off a crypto theft of about $6.34 billion — and the front door was not a supercomputer or an exotic zero-day. According to Engadget’s reporting, the intrusion into Binance began months earlier with two painfully ordinary tricks. In June, a wallet infrastructure engineer downloaded a tampered installer for an AI programming tool. In September, another engineer sat through two rounds of job “interviews”; the assignment file sent by the supposed CEO carried the malware. On October 20 the attackers used an internal AI tool to hop onto two more engineers’ machines, and on October 29, with stolen credentials in hand, they ran the script that moved the money. The FBI attributed the attack to North Korea. Binance said about $2.85 billion was frozen, that it restored 98% of affected assets, and that it would absorb the loss. We tell the full story in our news coverage of the heist.
Read that again and notice what is missing: nobody “hacked the blockchain.” They hacked people’s habits — a download that looked routine, an interview that felt flattering, a file that seemed like homework. That is how almost every crypto scam works. Scams are not creative, though: they recycle a handful of patterns, and once you can name the pattern, most of the spell breaks. Here is the map.
Pattern 1: The fake exchange or “investment platform”
How it looks: A polished website or app — sometimes a near-perfect clone of a real exchange, sometimes an invented brand with a confident logo — where you deposit crypto and watch your “balance” grow on screen. Small withdrawals may even work at first, to build trust. Then comes the moment of truth: to withdraw your “profits,” you must first pay a tax, a verification fee, an unlocking charge. Each payment unlocks a new excuse, never your money.
The tell: The balance was never real — it was a number on a screen controlled by the scammer. Legitimate platforms do not charge surprise fees, demanded in advance and in crypto, to release your own funds.
Pattern 2: Seed-phrase phishing
How it looks: A support pop-up, a fake “wallet verification” page, a DM from “support,” an airdrop claim form — all roads lead to one request: enter your recovery phrase (also called a seed phrase) to “validate,” “sync,” “restore” or “secure” your wallet.
The tell: This one has no exceptions, so it is the easiest rule in all of crypto: no legitimate company, support agent or website will ever ask for your seed phrase. The phrase is the master key to everything in the wallet. Anyone who has it does not need your password, your phone or your permission — and transactions cannot be reversed.
Pattern 3: Pig butchering — the long, friendly con
How it looks: It starts with a wrong-number text, a friendly stranger on social media, or a dating-app match who seems almost too interested in you. Over weeks, the conversation warms up; eventually your new friend mentions, casually, how well their own crypto investments are doing — often with screenshots, often with a relative or “uncle” who “knows the market.” You are guided to Pattern 1’s fake platform, in friendly, unhurried steps. The name comes from the method: the victim is fattened with attention and small apparent wins before the slaughter.
The tell: The combination, not any single message. Romance or friendship plus investment advice plus a platform you had never heard of equals one conclusion, however kind the person seems. Real friends do not come with a deposit link.
Pattern 4: Fake giveaways and celebrity livestreams
How it looks: A livestream or post, apparently from a famous founder or a big exchange, announces a celebration: send 1 unit of crypto, receive 2 back. The video may be recycled real footage; the account may be hacked or impersonated; the grateful comments are bots.
The tell: Arithmetic. Nobody doubles money for strangers as a marketing strategy. The moment a “giveaway” requires you to send crypto first, it is not a giveaway — it is a collection box with your name on the wrong side of it.
Pattern 5: Impersonation and job-interview lures
How it looks: This is the pattern that opened the door at Binance. Fake recruiters approach people who work — or want to work — in tech and crypto. There are interviews, sometimes several, all professional. Then comes a “technical assignment,” a “coding test,” or a tool to install for the next round. The file is the attack: malware that steals credentials, session tokens and wallet access. Variations include fake support agents and fake “security teams” from your exchange asking you to “verify” activity.
The tell: The process moves you off official channels and asks you to install or open something unusual. Real hiring processes are slow, bureaucratic and allergic to improvisation; a recruiter who sends you an executable file is not a recruiter. Treat every unexpected download from a stranger as hostile until proven otherwise.
The red-flag checklist
Whatever the costume, scams keep reusing the same wardrobe. Slow down and count how many of these appear:
- Urgency. “Act now,” “offer expires,” “your account will be closed.” Urgency is the anesthetic that stops you checking.
- Guaranteed or unusually steady returns. Markets wobble; scammer dashboards only go up.
- A move to private channels. The conversation insists on leaving the official app, site or email thread.
- Payment to unlock payment. Fees, taxes or “verification deposits” before a withdrawal.
- Any request for your seed phrase, private key or a screen-share of your wallet. One occurrence is enough — this is the whole ballgame.
- A download you did not go looking for. Installers, “assignments” and tools sent by someone you met online.
One red flag deserves a pause. Two deserve an exit.
How to protect yourself: the boring steps that work
Scam defense is unglamorous, and that is precisely why it works — it does not depend on spotting the fake in the moment.
Keep long-term holdings in self-custody, on a hardware wallet. Coins held on an exchange are an IOU from that exchange; coins in a wallet whose keys never touch the internet are immune to entire categories of remote theft. A hardware wallet keeps your keys on a small physical device and asks you to confirm transactions on the device itself, so malware on your computer cannot quietly sign your money away. If the idea is new to you, start with our beginner’s guide to hardware wallets — it explains what these devices do, and just as importantly, what they cannot do. Two widely used entry points are below. A hardware wallet cannot protect you if you hand over the seed phrase yourself — which is why Pattern 2 matters.
As an Amazon Associate I earn from qualifying purchases. The devices below are presented as research-based picks — we have not hands-on tested them — and buying through this site’s product links is always optional; the protection advice above works the same wherever you buy.
Ledger
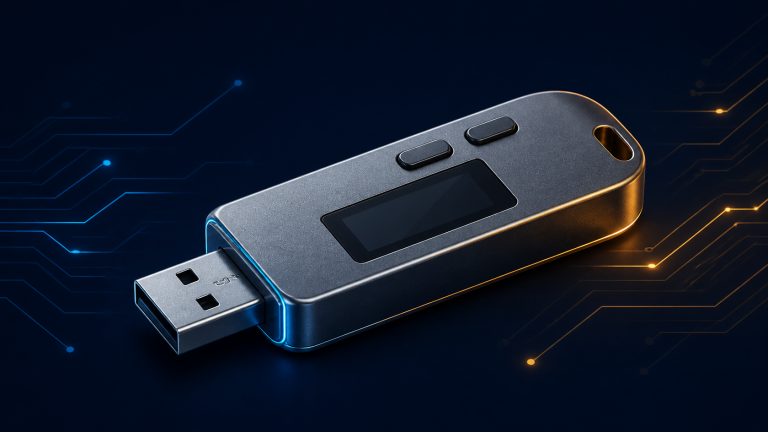
Ledger Nano S Plus
The Ledger Nano S Plus is Ledger's wired, entry-level signer for desktop and Android users who want offline key storage without wireless features.
- Secure Element: ST33K1M5, CC EAL6+ certified
- Display: 1.1" monochrome OLED 128×64
- Connection: USB-C only (desktop and Android); no Bluetooth
As an Amazon Associate I earn from qualifying purchases.
Trezor
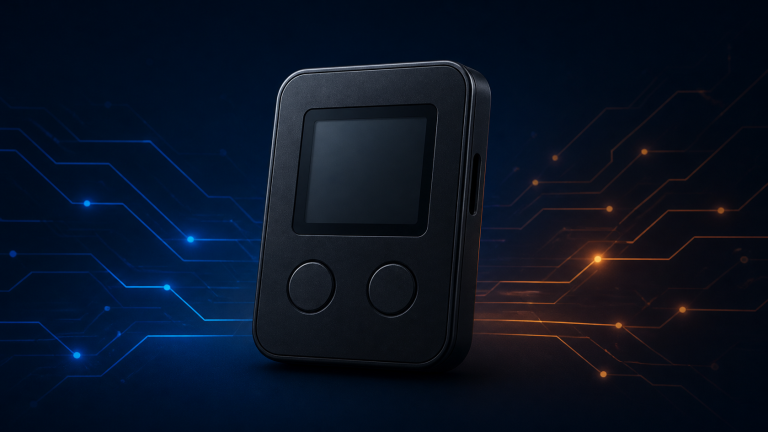
Trezor Safe 3
The Trezor Safe 3 is Trezor's entry-level Safe-series wallet, combining its open-source design approach with a certified Secure Element for the first time in its entry line.
- Secure Element: OPTIGA Trust M (V3), CC EAL6+
- Display: 0.96" monochrome OLED 128×64, two buttons
- Connection: USB-C only (power and data; USB-C to USB-C cable included); no Bluetooth
As an Amazon Associate I earn from qualifying purchases.
Guard the seed phrase like the master key it is. Write it on paper (or stamp it in metal), store it offline, and never type it into a website, photograph it, or keep it in cloud notes. If any service “needs” it, the service is the scam.
Use strong account security on exchanges and email. Unique passwords (a password manager makes this painless), two-factor authentication with an authenticator app or a hardware security key rather than SMS, and withdrawal address allowlists where the exchange offers them. Your email account is the skeleton key to everything else — secure it first.
Slow the money down. Bookmark the official sites you use and navigate from the bookmark, never from a message link. For any new address, send a small test transaction first and confirm it arrives. And adopt a house rule that defeats most urgency tricks by design: no crypto purchase, transfer or “opportunity” gets decided the same day it appears.
Keep your software boring too. Download wallets, tools and updates only from the official site you navigated to yourself; the Binance intrusion reportedly began with a tampered installer for a programming tool. If a download arrives attached to an opportunity, it is not a download. It is the attack, wearing a name tag.
The Bit Take
Scammers sell speed and certainty; crypto offers neither, which is why the honest tools are so dull: a hardware wallet, a phrase on paper, a day of waiting. The Binance heist started with a fake interview — so keep your keys offline, your skepticism online, and remember that no real opportunity has ever needed your seed phrase.
Sources
- Engadget — “Binance attackers used fake job interviews to pull off $6.3 billion crypto heist.” Published November 4, 2026. https://www.engadget.com/2306223/binance-attackers-fake-job-interviews-6-3-billion-crypto-heist/
Ledger Nano S Plus
Check price on Amazon